news

Log4j is not used in any Carmenta product


Published on: 2021-12-21

Posted in: Carmenta Engine, Carmenta Map Builder, Carmenta Server, Carmenta Server Core, Company

Recently there has been a large focus in the media on a discovered critical security vulnerability CVE-2021-44228 in the Java library Log4j. Log4j is not used in any Carmenta product.

Related news

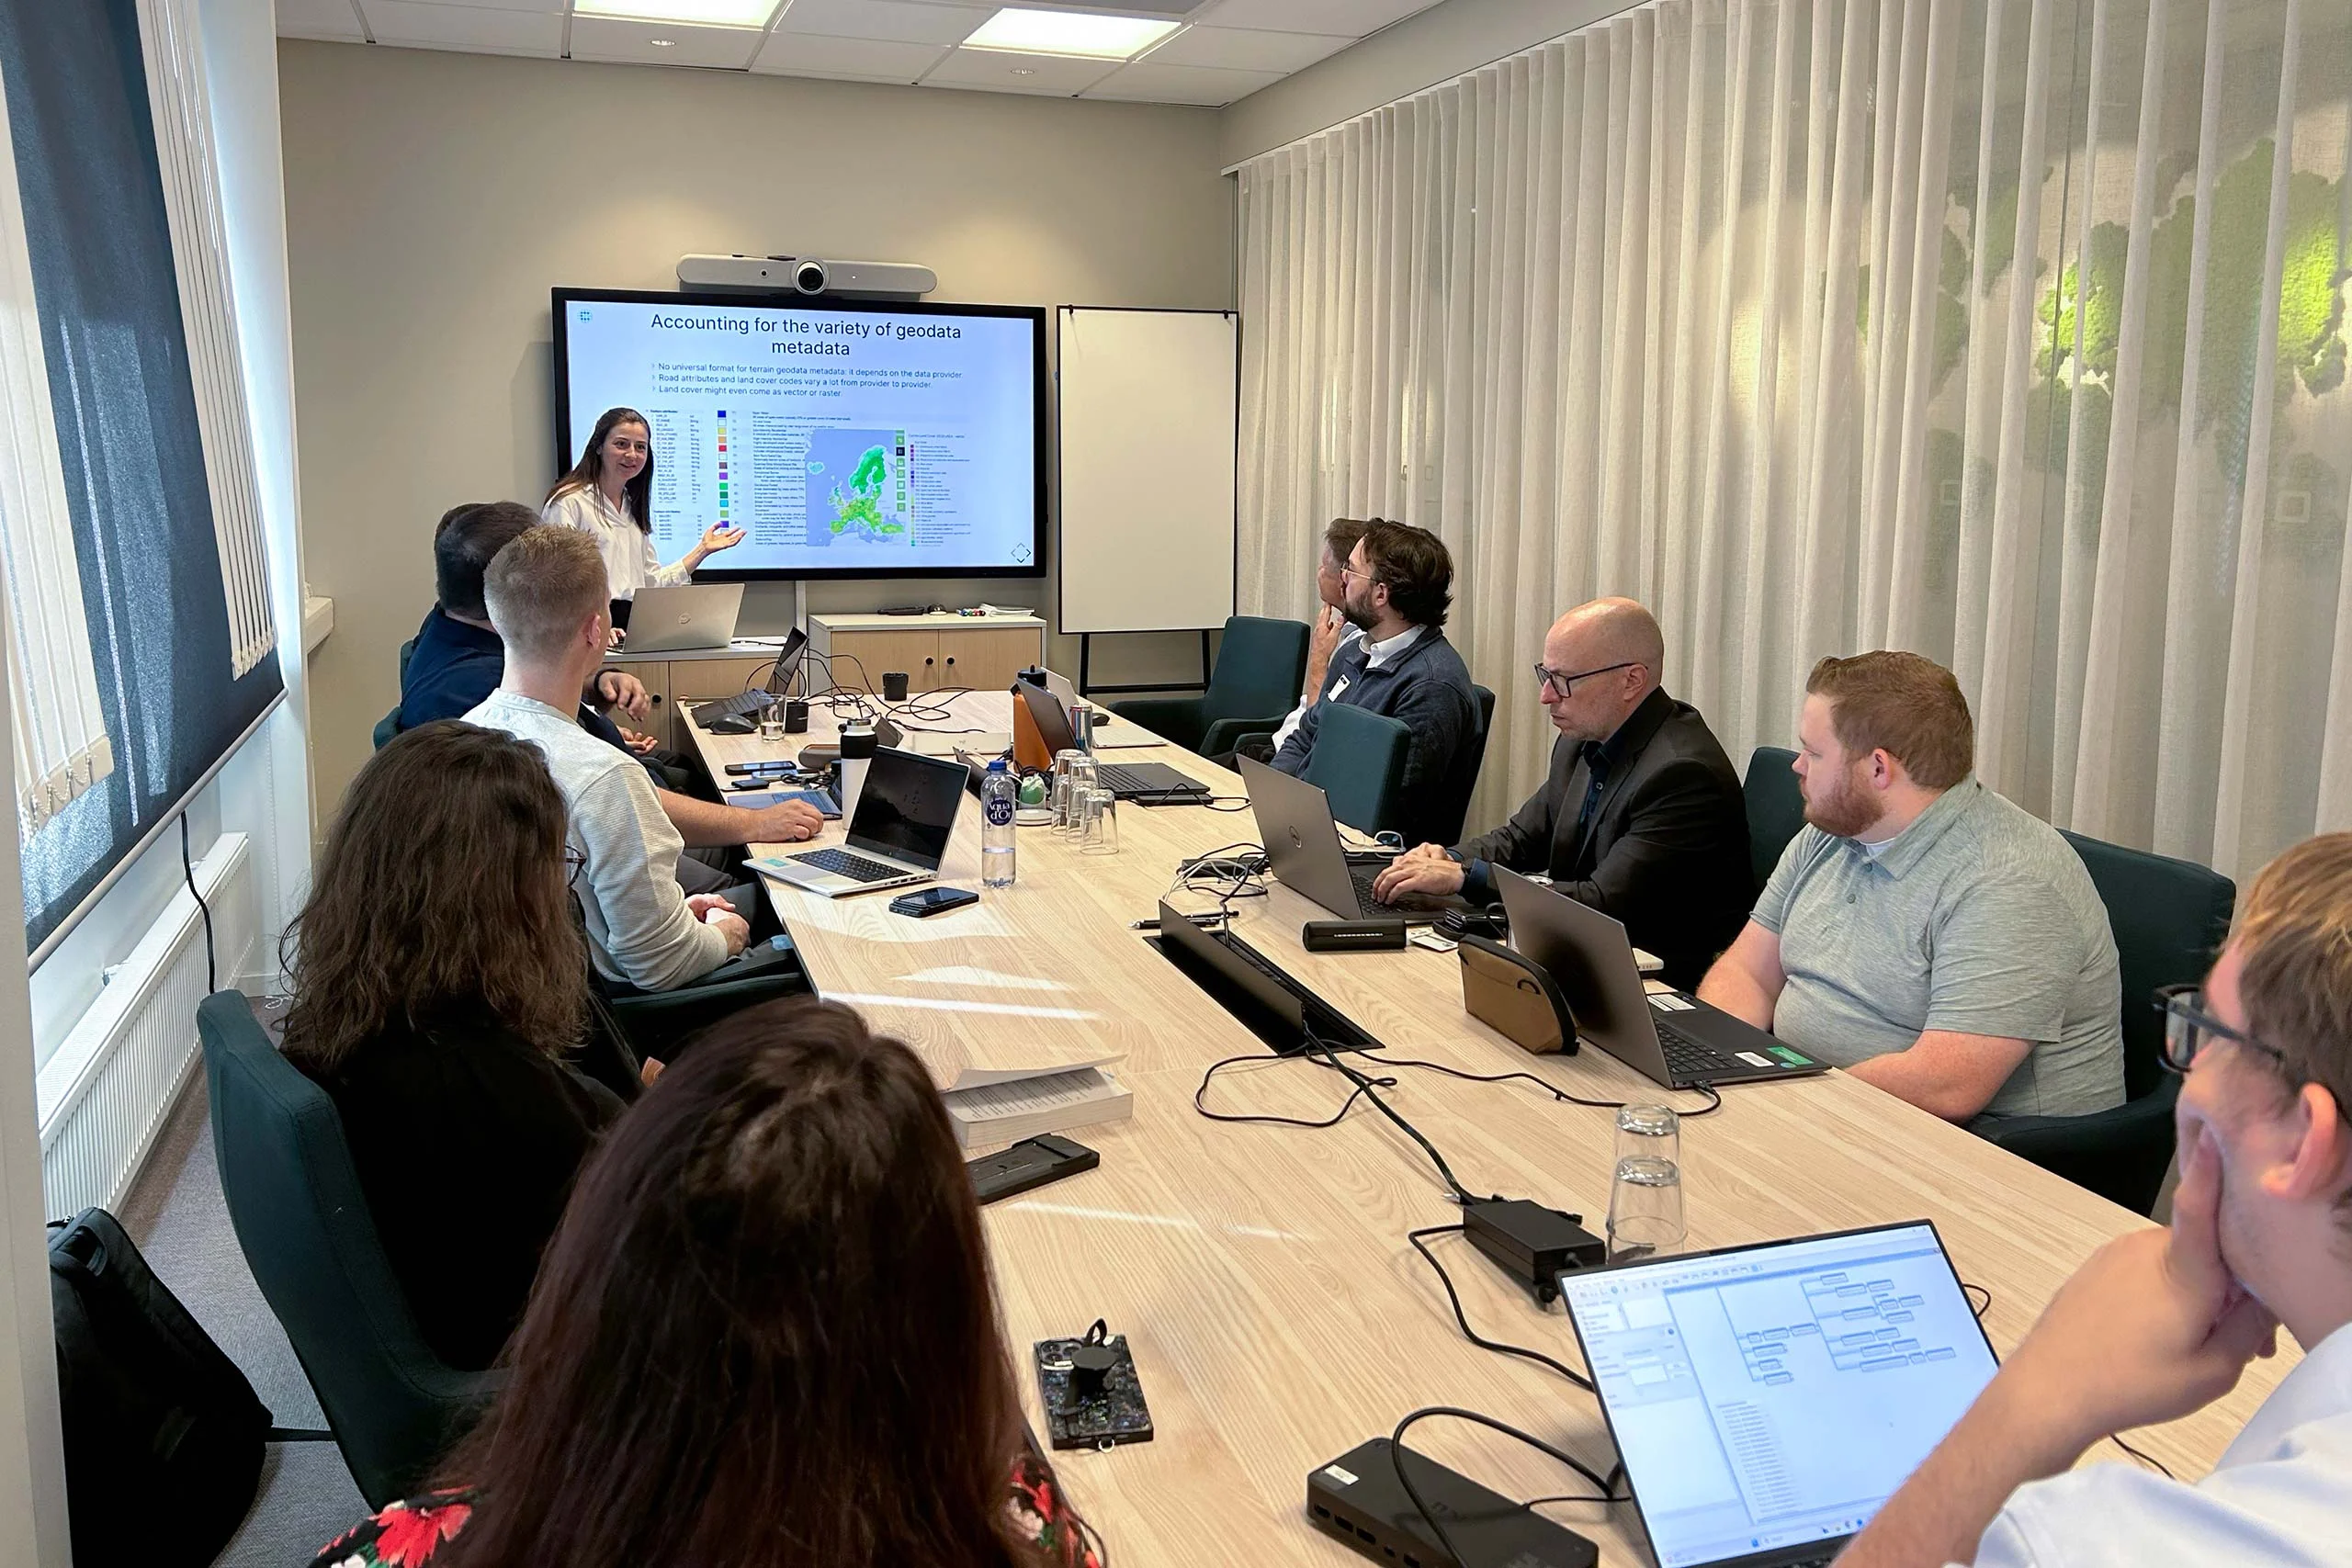
Training session in Carmenta Engine and Carmenta UAS Mission Kit during the NSWC Crane and TRISTAR visit

Carmenta Selected for the U.S. FCT Program

Following a recent visit from the U.S. Naval Surface Warfare Center, Crane Division (NSWC Crane), and TRISTAR to Carmenta's Gothenburg office, we would like to share more about the Foreign Comparative Testing (FCT) Program behind our ongoing collaboration.

Read more
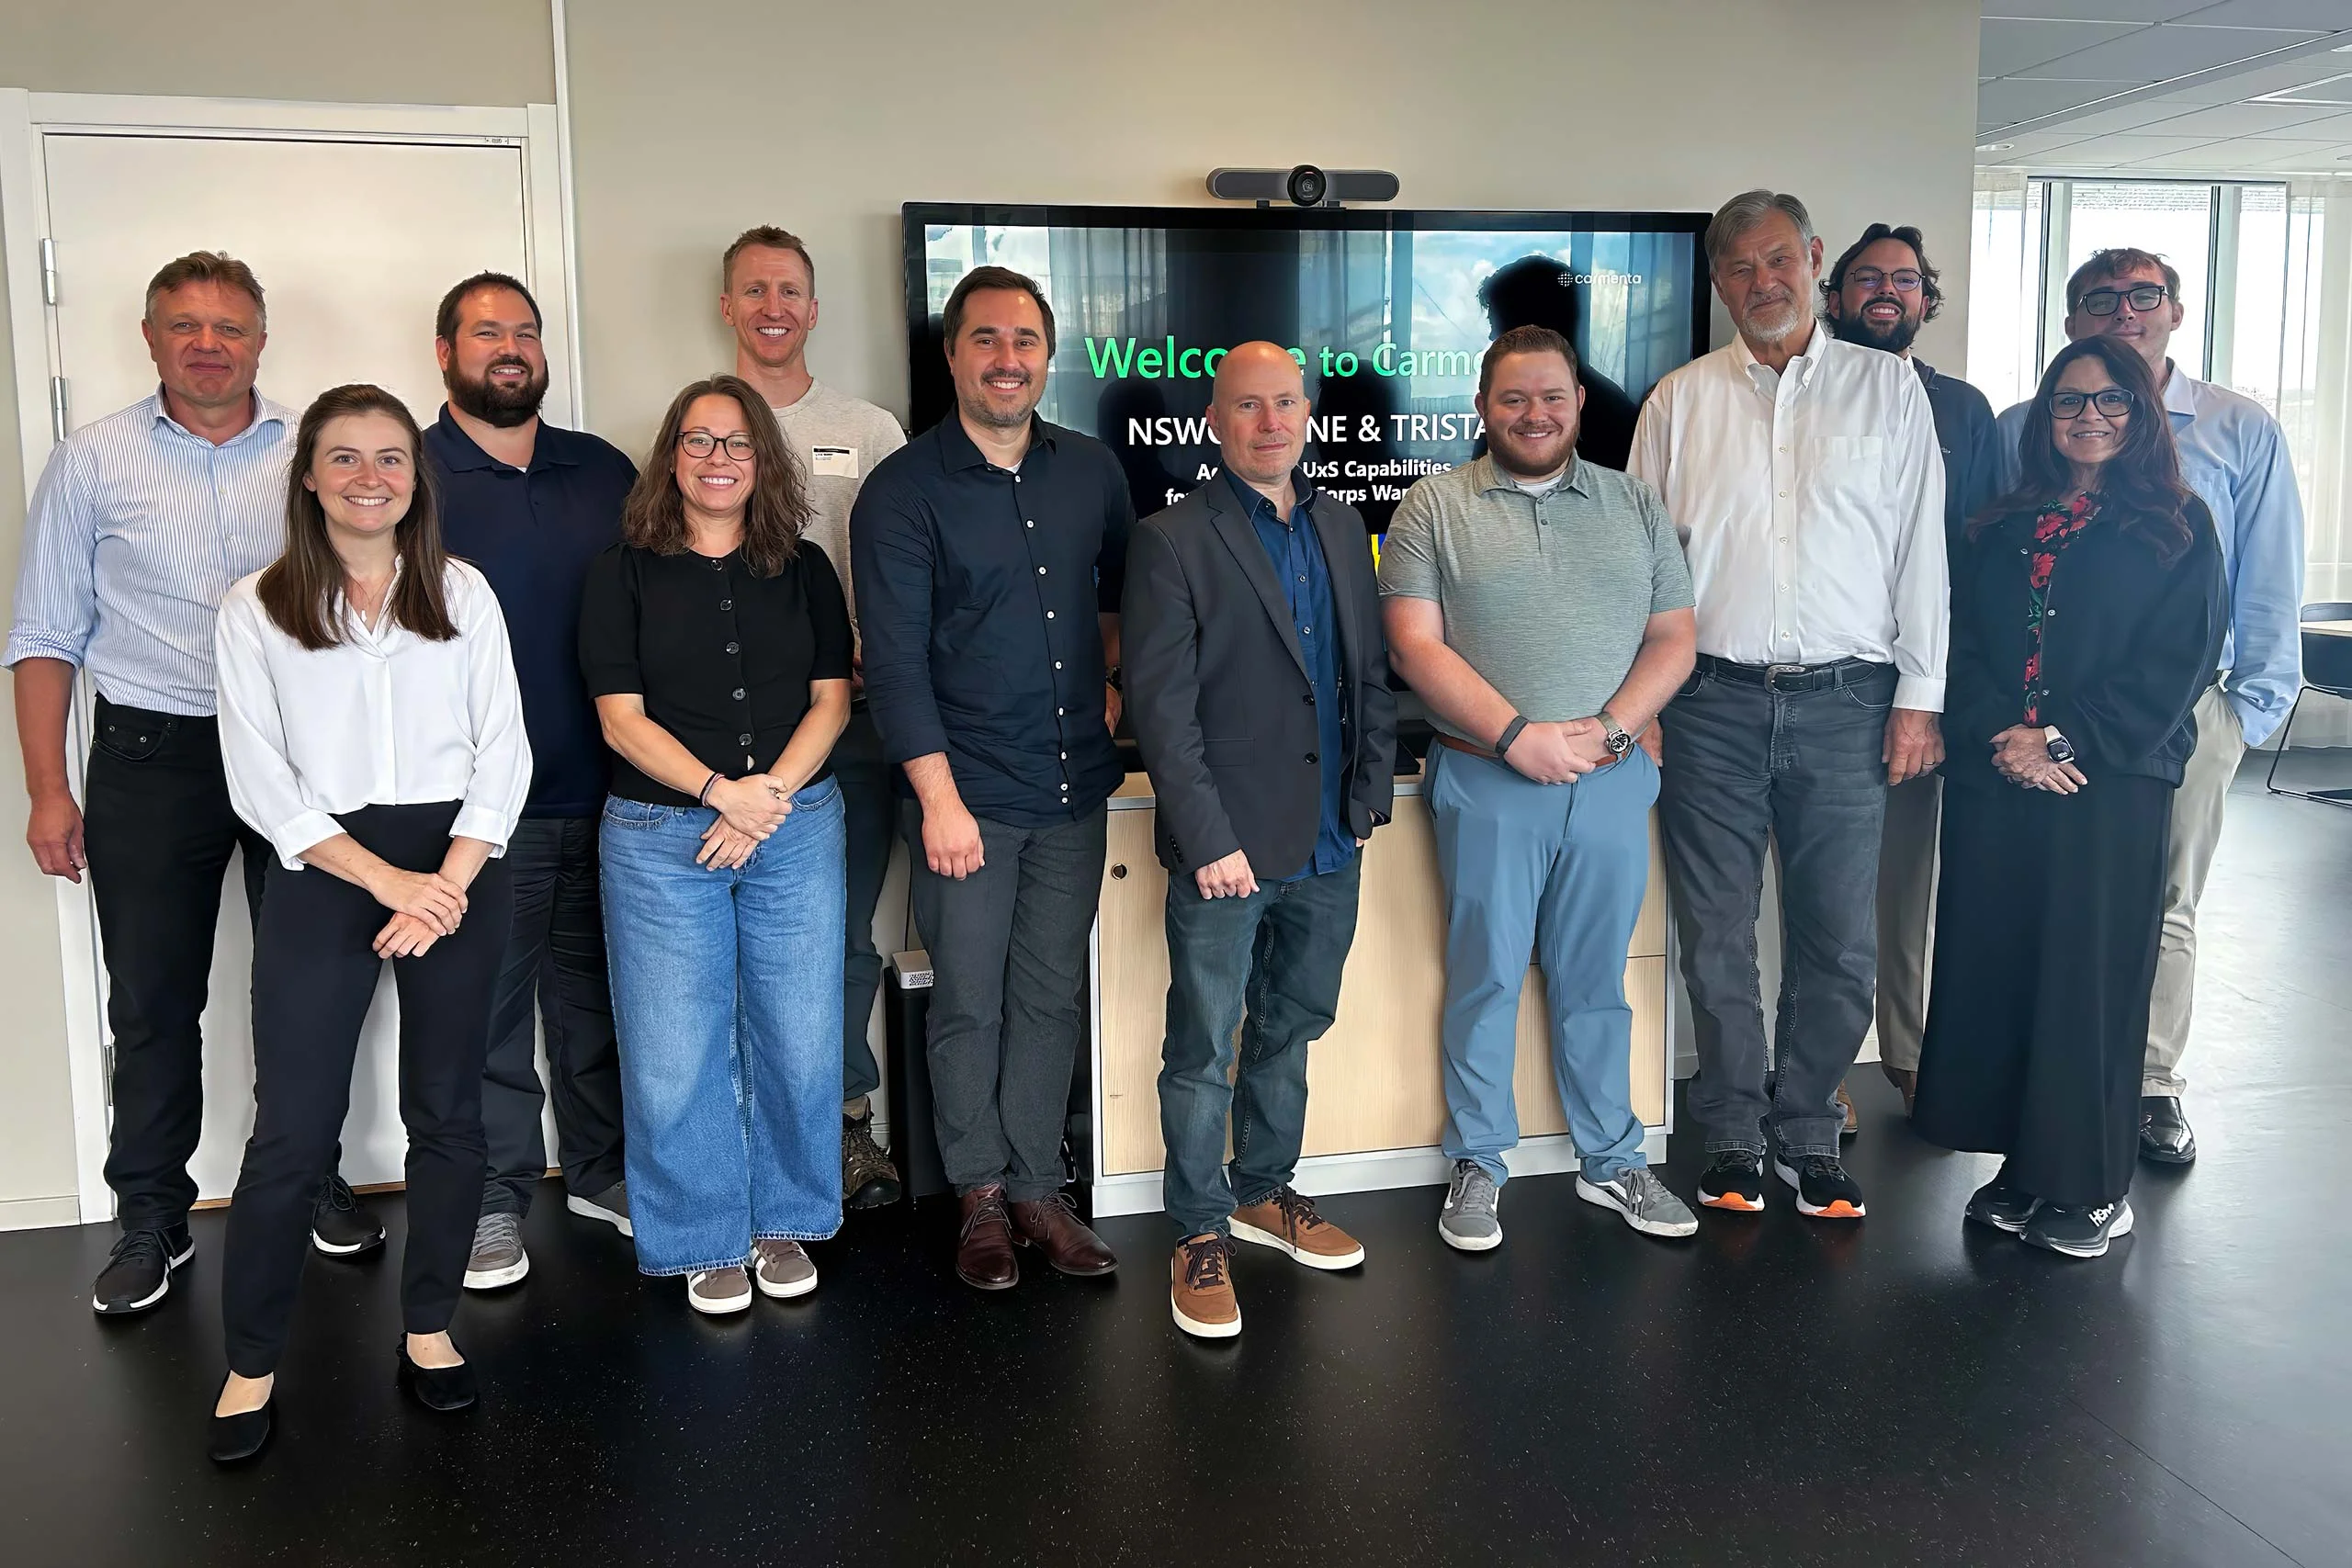
The NSWC Crane, TRISTAR, and Carmenta team during the training at Carmenta

NSWC Crane and TRISTAR visit Carmenta

Representatives from the U.S. Naval Surface Warfare Center, Crane Division (NSWC Crane) and TRISTAR recently visited Carmenta for a week of hands-on training to advance multi-domain UxS capabilities for the U.S. Marine Corps.

Read more